Real-Time Protection
The real-time scanner watches the directories of every cPanel account through the Linux kernel. When a file is created, changed or moved in, it is scanned right away and the automatic action is applied: known malware is quarantined by default, injected code can be removed with Auto Clean, and suspicious files are reported for review.
This covers every way a file reaches the server — FTP, SFTP, a CMS upload form, an archive extracted on the server or a script that writes files — and new accounts are watched as soon as they are created.
Turning it on or off
The scanner is in Settings → Real-time protection. It is on by default.
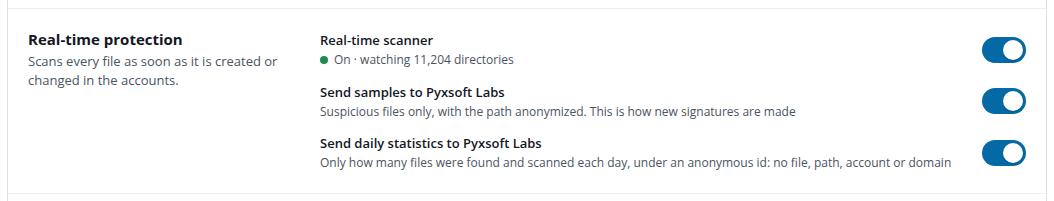
- Real-time scanner. The status line shows how many directories are being watched. When it is off, new files are only checked by the scans, and the Overview warns about it.
- Send samples to Pyxsoft Labs. Suspicious files only, with the path anonymized. This is how new signatures are made, and how a suspicious file found on your server can be confirmed as malware later.
- Send daily statistics to Pyxsoft Labs. Only how many files were found and scanned each day, under an anonymous id: no file, path, account or domain.
Changes apply when you click Save changes.
What it detects
- Known malware, by signature: web shells, backdoors, droppers, injected code, mailers and more.
- Suspicious files, flagged by the Pyxsoft heuristics when there is no signature yet, including phishing kits. When Pyxsoft Labs publishes a signature for a file that was only suspicious, the detection becomes malware and gets the malware action.
- Dangerous symbolic links: broken links, and links pointing to system directories or outside the account. These are used to read other accounts' files or system configuration. You can allow links to the system or external links in Settings.
Servers with many directories
The Instant Scanner watches each directory through the Linux kernel, which limits how many directories can be watched at once (fs.inotify.max_user_watches). When a server reaches that limit, the scanner keeps watching every directory that fits and logs this message once:
The real-time scanner reached the inotify limit (fs.inotify.max_user_watches): some directories are not watched.
The directories left out are still covered by the global scan, but changes in them are not caught in real time. To watch them as well, raise the limit and restart the service:
echo fs.inotify.max_user_watches=1048576 > /etc/sysctl.d/90-pyxsoft.conf
sysctl --system
systemctl restart pyxsoft
Each watched directory uses about 1 KB of kernel memory, so a limit of 1,048,576 costs at most around 1 GB, and only for directories actually watched.